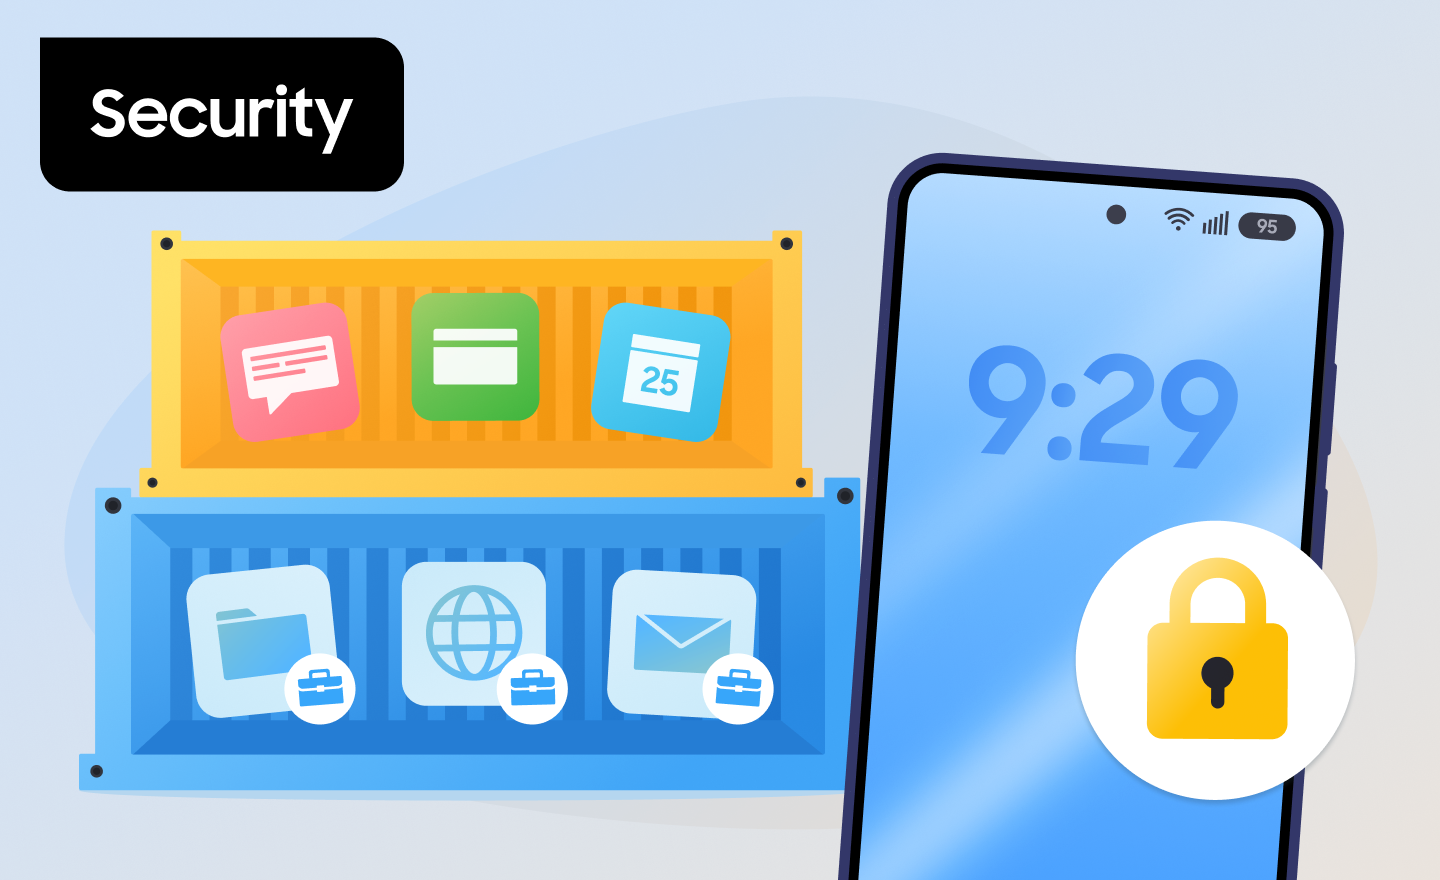
If you’ve spent time around IT or security teams, you’ve probably heard “containerization” used in two different conversations—and the overlap causes real confusion.
Developers use it to describe how software gets packaged. Security and mobility teams, however, use it to describe how a business keeps corporate data separate from the personal apps and photos on an employee’s phone. The two share a core idea, but only one of them matters when you’re deciding how to run a bring-your-own-device (BYOD) program.
Read on to learn what containerization means in enterprise mobility, how it works on a managed device, and where it fits alongside the mobile device management (MDM) tools you already run.
Table of contents:
- What is containerization?
- How does mobile containerization work?
- The benefits of containerization
- Containerization and MDM: how they work together
- Building a secure mobile workforce
What is containerization?
Containerization is the practice of packaging applications and data into an isolated unit that runs separately from everything around it. What that looks like depends on which kind you mean.
In software development, containerization bundles application code with its libraries and dependencies into a portable unit. Because the container shares the host machine’s operating system (OS) kernel instead of running its own, it stays lightweight and starts quickly.
In enterprise mobility and cybersecurity, the same principle is applied to a different problem: letting an employee use one phone for work and personal life without the two mixing. A container on a mobile device holds corporate apps, email, and files, and keeps them separated from personal content on the same hardware.
The rest of this guide covers that second meaning.
How does mobile containerization work?

Mobile containerization works by creating a separate, managed space on the device (commonly an Android Enterprise work profile) and enforcing rules about what can cross the boundary between that space and the personal side of the device.
Work apps live inside the container. Personal apps live outside it. IT manages what’s inside; on employee-owned devices, IT has no visibility into what sits outside the work profile.
That boundary is where the security value sits. If a personal app is compromised, the container is designed to keep that problem from reaching corporate email, files, and credentials. It runs the other way too: personal browsing history and photos stay outside the reach of corporate policy.
Admins can set granular rules about what moves across the line—apps, files, clipboard contents, contacts, calendar events, notifications, and messages. That granularity is what makes containerization workable for BYOD and hybrid work: IT doesn’t have to choose between managing the entire device or managing none of it.
The benefits of containerization
For enterprise mobility teams, the benefits of containerization come down to separating corporate risk from personal device use. Four stand out:
-
✔Data separation: Corporate apps and data sit apart from personal content, which helps reduce the risk of business information being exposed through an unmanaged or compromised personal app.
-
✔Employee privacy: On employee-owned devices, corporate policy applies to the work container only. Personal apps, photos, and browsing stay outside the managed environment.
-
✔Cleaner offboarding: When an employee leaves or a device goes missing, IT can remove the work container and its data without wiping personal content.
-
✔Consistent policy: The same data-separation rules can be applied across a managed fleet instead of device by device.
In software development the benefits look different—portability and scalability rather than data separation—but the underlying trade is the same: isolate something so a problem in one place stays in one place.
For teams building out BYOD security policies, containerization is usually the control that makes a dual-use device viable in the first place.
Containerization and MDM: how they work together
Containerization and MDM aren’t alternatives. The container is the space; the management platform is what creates it, configures it, and acts on it.
An MDM, enterprise mobility management (EMM), or unified endpoint management (UEM) platform provisions the work profile during enrollment, pushes the policies that define what the container allows, and handles remote actions when a device is lost or an employee leaves. Without a management platform behind it, a container doesn’t do much.
Most organizations already run one. So, the practical question usually isn’t which platform to buy—it’s how much control you actually get over the container once it exists.
Where Samsung Knox fits
Samsung Knox, Samsung’s all-in-one package of enterprise device security and management solutions, handles containerization through one component in particular. Knox Platform for Enterprise builds on Android Enterprise’s work profile architecture and adds more granular management policies on Samsung Galaxy devices.
Those policies reach your existing console through Knox Service Plugin, Samsung’s OEMConfig-based tool, which makes Knox Platform for Enterprise controls available in your EMM as new features ship. If you’d rather manage containers from a Samsung console instead, Knox Manage handles work profile management directly.
What containerization doesn’t cover
Containerization draws a boundary. It doesn’t inspect what happens inside it.
- A compromised app inside the container is still a work problem. Containerization limits the blast radius; it doesn’t replace endpoint security or data loss prevention.
- The container depends on the device underneath it. If the OS or boot chain is tampered with, the separation guarantees weaken. This is where hardware-backed protection matters: on Galaxy devices, work profile encryption keys are tied to a hardware root of trust, and work data is designed to become inaccessible if the device is detected as compromised.
- Employees have to actually use it. A work profile that people route around (forwarding files to personal email, for instance) separates less than the policy suggests.
Building a secure mobile workforce
Containerization is a way of drawing a clean line between what needs protecting and everything else. For organizations running BYOD or hybrid programs, it’s the control that makes a dual-use device workable: employees keep their phone, and the business keeps control of its data.
It works best as one layer among several—paired with a management platform that can enforce policy, and a device platform that can vouch for its own integrity.
Ready to see how containerization works on Galaxy devices?


